Every access decision leaves evidence
Who has access, why do they have it, who approved it, and can we prove it later?
Access is easy to grant — harder to explain later
Access requests travel through ticket queues, chat messages and inboxes. The grant happens somewhere, but the reasoning does not always survive it.
When a reviewer or auditor arrives later, teams reconstruct history from memory and exports. They can see that access exists, but not always why it was granted, who approved it or whether it is still justified.
From request to access — with the reasoning attached.
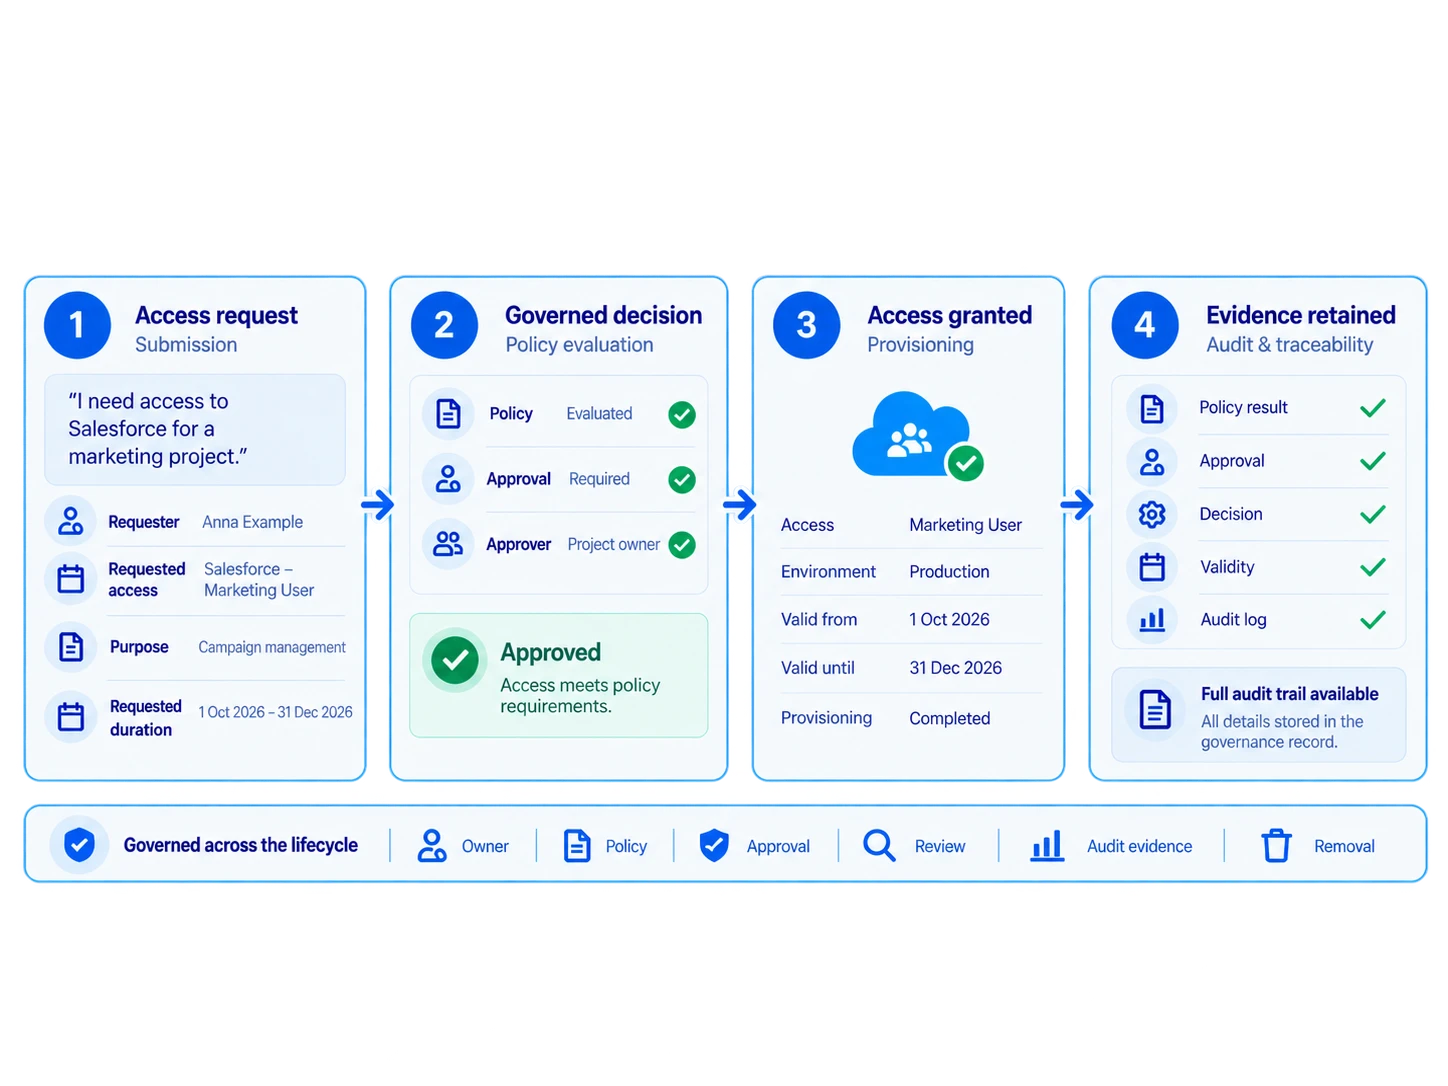
Seafront keeps policy evaluation, approvals, access reviews and audit evidence within the same governed process.
Each request is evaluated against policy, required approvals are recorded and the resulting access stays connected to the decision that justified it — giving reviews and audits the evidence they need later.
Built into the platform
Requests, policy evaluation, approvals and access reviews are part of the same governed control plane that governs employees, external users and AI agents. Access reviews draw on the same governed records, so reviewers see why access exists — the request, the policy result and the approval — instead of only that it does.
Could you prove why every access exists?
Show us how access is requested and reviewed in your organisation, and we will show how Seafront records the reasoning alongside the result.