Connect identity governance to the systems that matter
Connect identity sources and target systems to Seafront without turning every new connection into a traditional integration project.
Connecting systems should not become a project of its own
Identity governance depends on connections to the systems where identities and access actually live. Traditionally, building those integrations can require significant development, custom logic and lengthy configuration before the first identity can be provisioned.
The challenge grows as the environment changes. New applications are introduced, APIs evolve and access models change. If every connection requires specialist development, integration becomes one of the biggest barriers to deploying and evolving IGA.
Connect once. Govern through the same identity model.
Seafront connects identity sources and target systems through configurable integration patterns, so new connections do not become custom development projects.
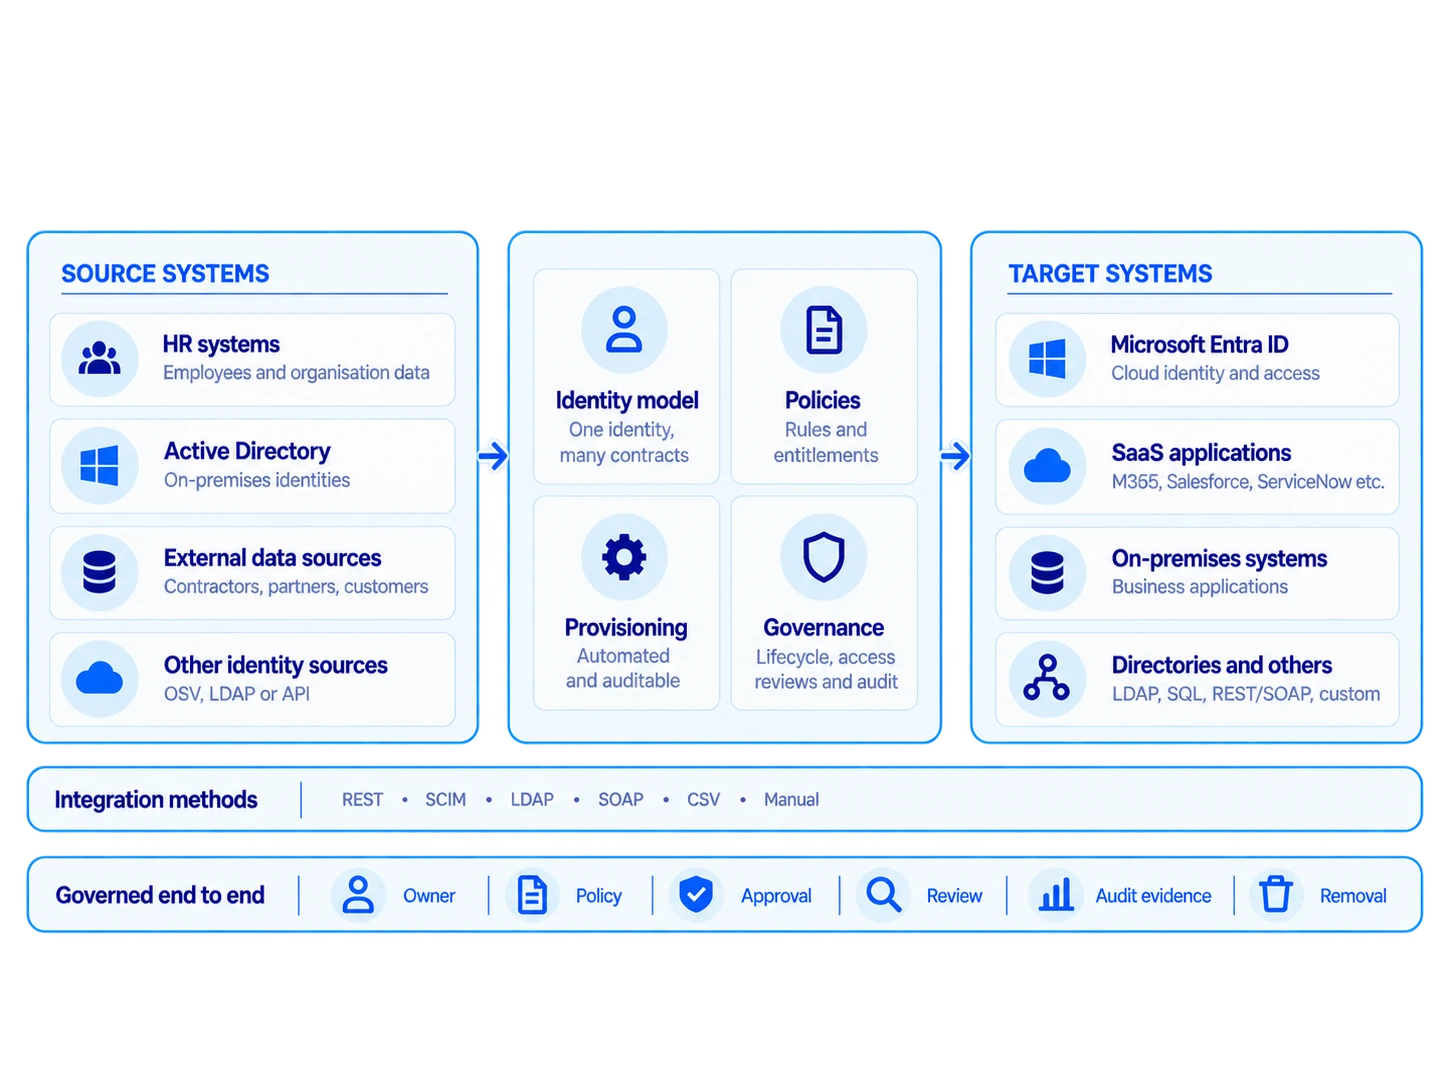
Standard interfaces and reusable configuration bring identity data in from source systems and provision governed access out to the systems that matter.
Built into the platform
Integrations connect Seafront to the systems where identities originate and where access is used. The same identity, contract and policy context can then drive governed provisioning across connected systems.
What would you connect first?
Show us your identity sources and target systems, and we will show you how Seafront can connect them without a traditional integration project.