External users without governance gaps
Employees usually have HR as their source of truth. Contractors, suppliers, consultants and partners often do not. Seafront brings them under the same governed identity lifecycle.
External users are easy to add — and easy to forget
External identities are often created quickly, under time pressure, by someone who needs the work to start. But there may be no authoritative source describing who the person is, why they are here, who is accountable for them or when their access should end.
Assignments finish quietly. Sponsors change roles. Accounts stay active. Over time, organisations accumulate external access that nobody can confidently explain or justify.
External access needs a reason, an owner and an end date.
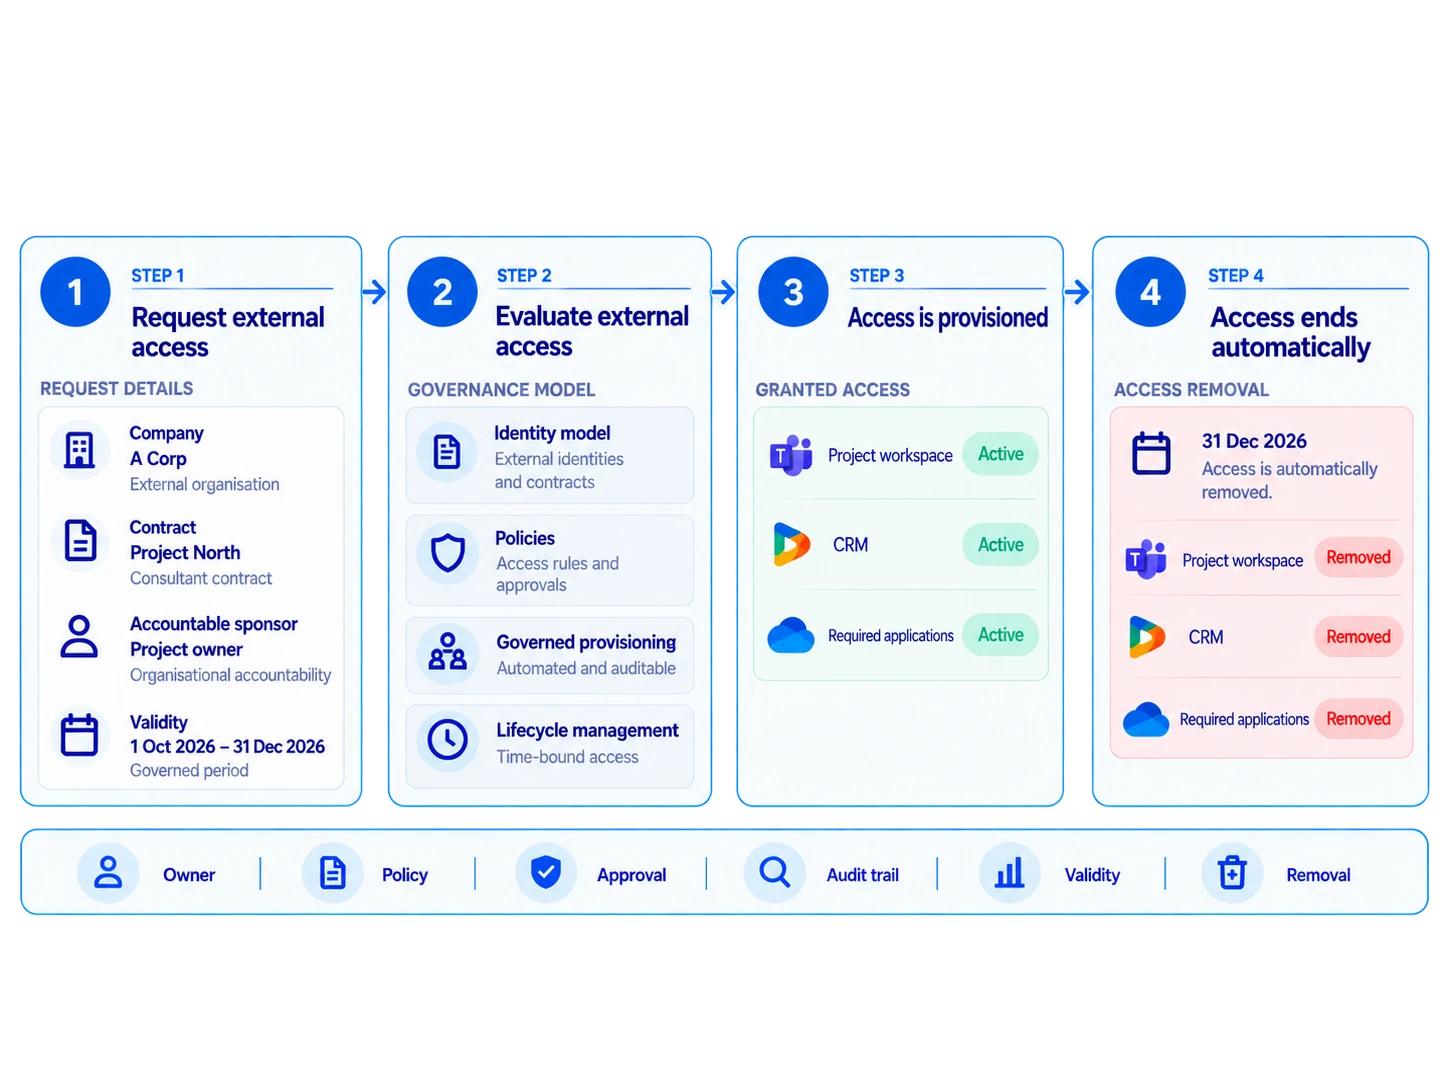
Seafront connects every external identity to the company, contract and accountable sponsor that justifies its access.
Validity dates define how long that relationship remains active, so access is governed from onboarding through automatic removal when the contract ends.
Built into the platform
External identities use the same governed identity model as employees, while adding the company, contract, sponsor and validity context needed for external access governance. Sponsors can be asked to confirm continued need, and every extension or removal is recorded as a governed decision rather than an informal favour.
How many external identities are still active today?
Tell us how contractors and suppliers are onboarded in your organisation, and we will show how Seafront keeps their access bounded.