Access that follows every relationship
Give people the right access from day one, keep it aligned as roles and relationships change, and remove it when the relationship ends.
Access rarely follows organisational change automatically
Joining, moving and leaving are ordinary business events, yet access often depends on a chain of manual requests. New starters wait for access. People changing roles accumulate permissions. And when a relationship ends, access can remain active long after it should have been removed.
The problem is not a lack of intent. It is the missing connection between a person’s relationship with the organisation and the access that relationship should justify.
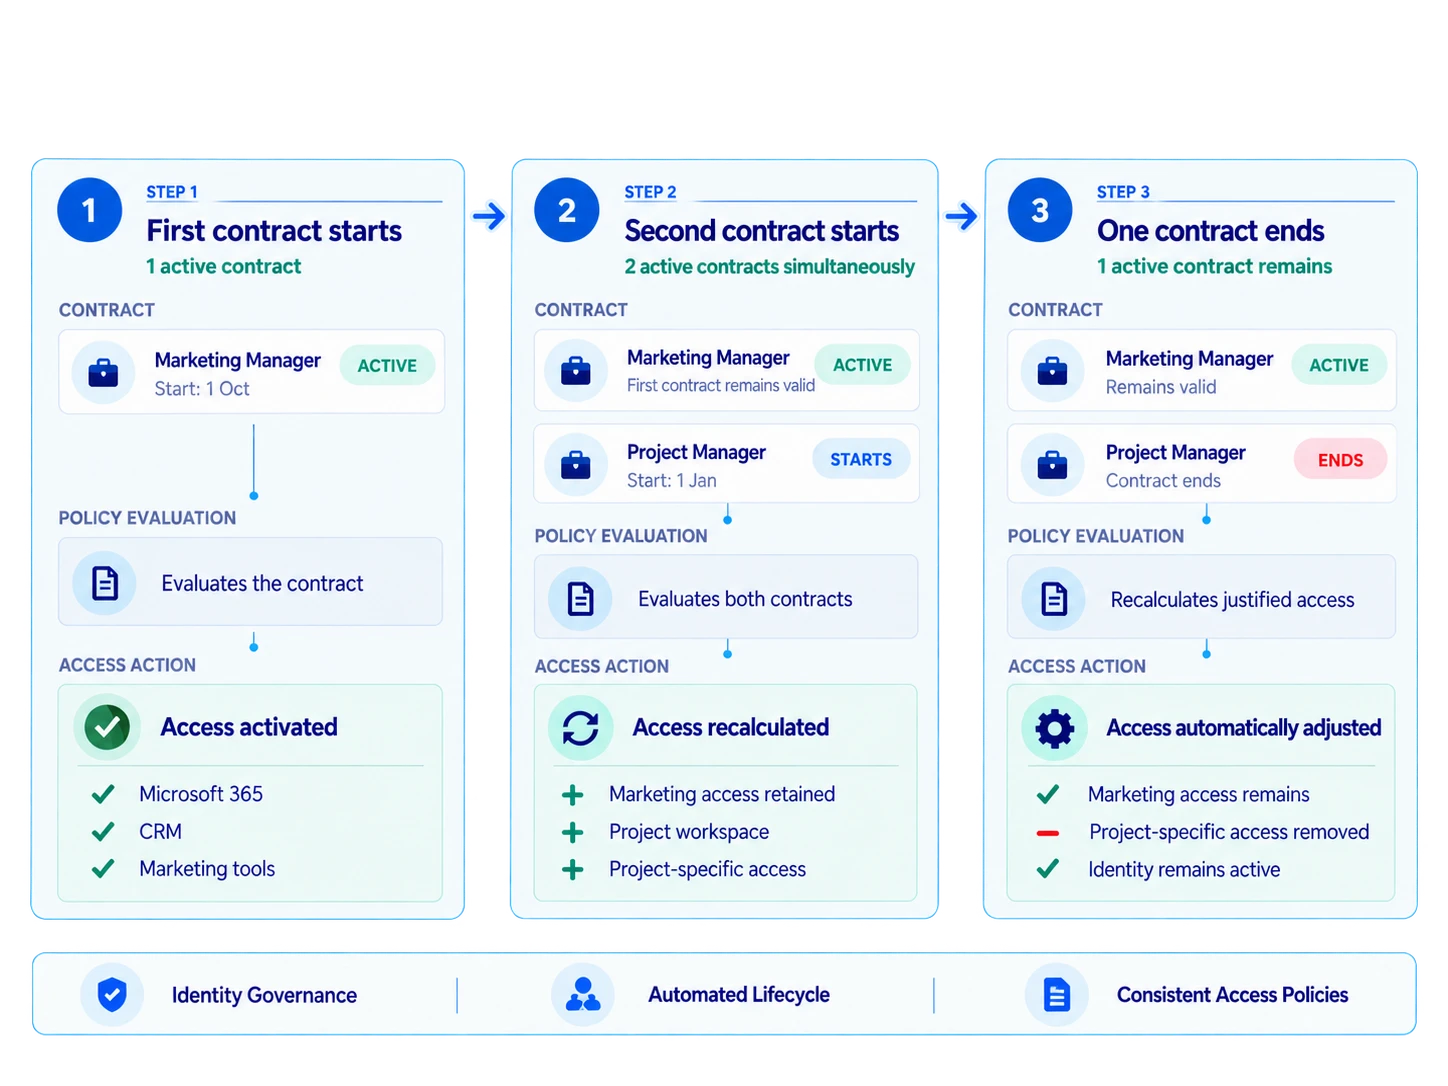
One identity. Many contracts. Access follows each one.
Seafront connects identity and access to the relationship that justifies it. When a relationship starts, changes or ends, Seafront triggers the appropriate identity and access actions automatically.
A person can have multiple valid contracts at the same time. Each contract is evaluated against your policies and approvals, so access changes are automatic, governed and auditable.
Built into the platform
Lifecycle rules, policy evaluation and provisioning run on the Seafront platform, so the same controls apply to employees, external users and non-human identities. Changes can be described in natural language and verified through simulation before anything reaches a target system.
Ready to make joiners, movers and leavers routine?
Tell us how employment data flows in your organisation, and we will show how Seafront could drive the lifecycle end to end.