Make access governance easier to prove.
Seafront helps you demonstrate how access is granted, reviewed and removed. Connect identities, access decisions and accountable owners with the evidence needed for internal controls, regulatory requirements and audits.
Policies need evidence behind them
A documented access policy is only the starting point. Organisations also need to show how that policy is applied: why access was granted, who approved it, whether it remains necessary and what happened when the need ended.
When those answers are spread across spreadsheets, tickets and separate systems, preparing for an audit becomes a manual reconstruction exercise. The same questions now extend to external users, service accounts and AI agents.
Build evidence into everyday identity governance
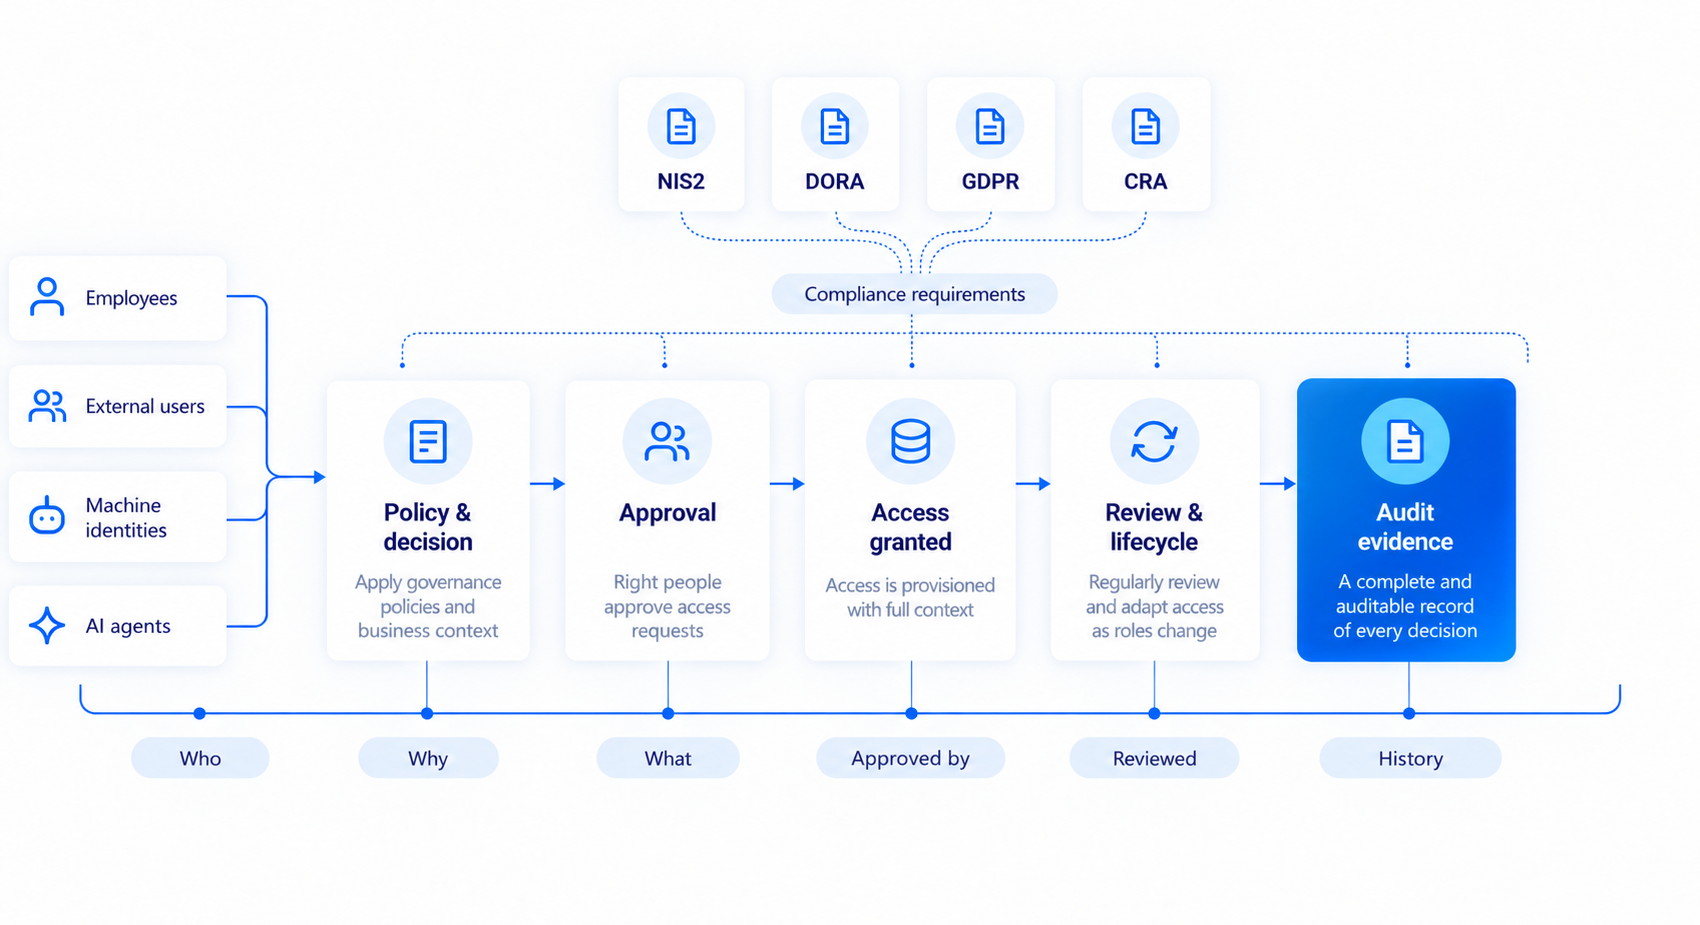
Seafront brings identity context, policies, approvals, access reviews and lifecycle controls into the same governed process. Access stays connected to the reason it exists and the decisions made throughout its lifecycle.
That gives security teams, application owners and auditors a clearer basis for understanding and verifying access.
 View illustration full size (opens in a new tab)
Explain why access exists
Connect access to a person’s role, contract or business need. For machine identities and AI agents, establish an accountable owner and a defined purpose.
Record decisions and approvals
Keep policy evaluations and required approvals connected to the resulting access, so the reasoning remains available for later review.
Review continued access
Use access reviews to assess whether permissions are still appropriate and record the decisions made by reviewers.
Manage changes and removal
Update access as roles, contracts and needs change. Use lifecycle controls to remove access when its basis ends.
Maintain an audit trail
Preserve a traceable history of governance decisions, approvals, reviews and changes to support audits and internal investigations.
Support the identity controls behind compliance
Different regulations address different risks, but identity governance provides a practical foundation for controlling access and demonstrating accountability. Seafront supports the identity and access governance part of your compliance programme.
NIS2
Support access governance within your cybersecurity risk management programme. Seafront helps organisations apply access policies, manage identity lifecycles, review permissions and retain evidence of governance decisions.
DORA
Support identity and access governance within financial-sector ICT risk management. Governed approvals, access reviews and lifecycle controls help organisations manage permissions and demonstrate how access decisions are administered.
GDPR
Support the protection of personal data through controlled access. Seafront helps organisations govern who receives access to connected systems, review whether that access remains appropriate and maintain evidence of related decisions.
Cyber Resilience Act
The CRA addresses the cybersecurity of products with digital elements and the responsibilities of their manufacturers. Identity governance can help control access to development and product-support environments. CRA product conformity, vulnerability handling and technical documentation remain separate responsibilities.
Seafront supports specific identity and access governance controls. Overall compliance depends on your organisation’s processes, configuration and wider security measures.
Accountability extends to AI agents
An AI agent or service account needs a clear owner, a defined purpose and access that can be justified. As these identities become more common, organisations need to review and manage their permissions throughout their lifecycle.
Seafront governs employees, external users, machine identities and AI agents through the same platform. This helps teams maintain consistent accountability and audit evidence across different identity types.
Explore AI Agent & Non-Human Identity GovernanceOne governance process, connected evidence
Compliance evidence comes from the same processes used to manage identities and access every day. Policies, approvals, reviews and lifecycle changes provide the context needed to explain governance decisions.
Explore how Seafront connects these capabilities across your organisation.
What would you need to show in your next audit?
Tell us about your access governance processes and compliance requirements. We will discuss how Seafront can help you manage identities, clarify responsibilities and build the evidence you need.