AI Agents Need Governed Access and Human Oversight
As AI agents take on tasks across business systems, organisations need a clear understanding of what those agents can access, who is responsible for them and when human approval is required.
23 September 2026 · 5 min read · Seafront team
At the same time, AI offers new ways to make Identity Governance and Administration (IGA) easier to configure and operate.
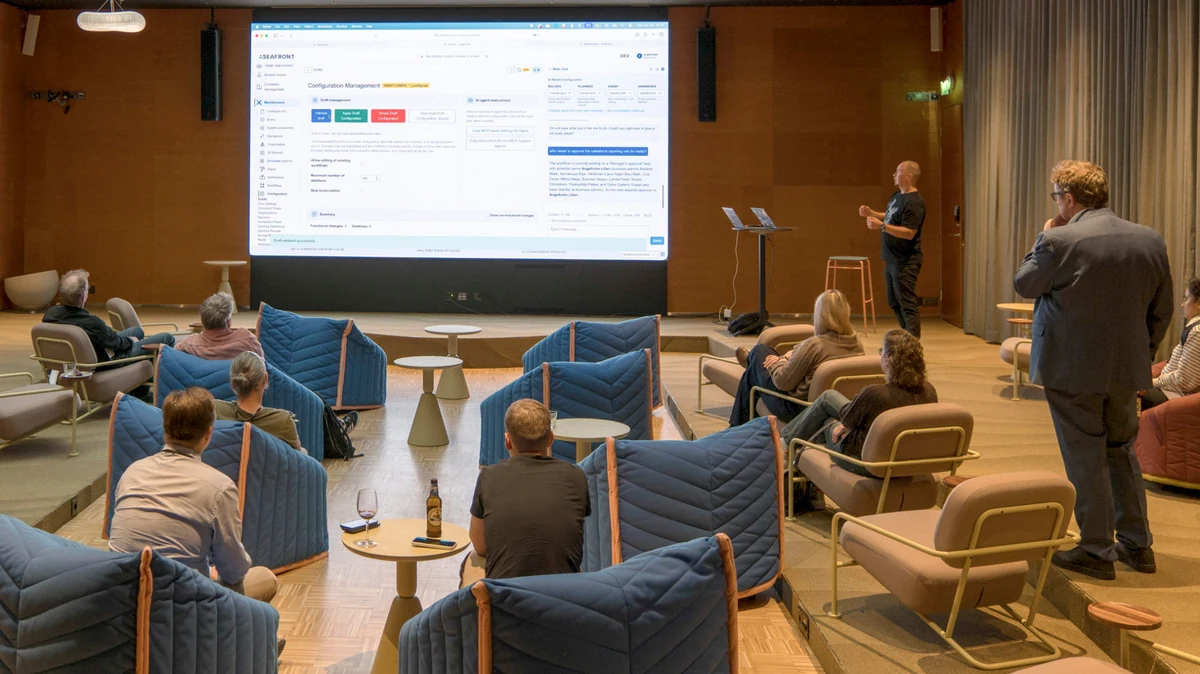
Both topics attracted interest at State of Identity Helsinki 2026. In the Seafront IGA demo room, Haidion’s Joonatan Henriksson and Joonas Jokinen demonstrated how these capabilities work in practice. The conversations reflected a practical need: organisations want to put AI to work while keeping access and responsibility under control.
Give every agent an owner, a purpose and appropriate access
An AI agent that reads documents, updates business records or calls an API needs access to perform its task. That access should have a clear business purpose and an accountable owner.
Organisations should be able to answer basic questions about every agent operating in their systems:
- Who is responsible for the agent?
- What is it intended to do?
- Which systems and data can it access?
- Which actions require human approval?
- When should its access be reviewed or removed?
These answers need to remain current as the agent’s role changes. An agent created for a short pilot should not retain access indefinitely. An agent given a new task may need different permissions. If its owner changes roles, responsibility needs to transfer to someone else.
Seafront IGA manages AI agents as identities with ownership, purpose and a defined lifecycle. Contracts provide the context for access, bringing agent permissions into the same governance processes used for other identities.
Keep people involved in consequential decisions
The level of human involvement should reflect what an agent is allowed to do.
An agent preparing a draft from approved reference material has a different risk profile from one updating sensitive records or taking action on behalf of a customer. Giving an agent permission to read information does not automatically justify permission to change it or share it externally.
Organisations therefore need to define where an agent can act independently and where a person must review or approve the next step. Reviewers need enough context to make that decision: what is being requested, why it is needed and what the consequences could be.
Identity governance supports this through access policies, approval workflows and records of governance decisions. Applications and connected systems must also enforce the relevant permissions and any approvals required for individual actions.
Human oversight is most useful when it is built into the process and focused on decisions that need judgement.
Use AI to simplify configuration and operation
AI also has a role in making governance easier to use.
Configuring integrations, understanding existing permissions and preparing access changes can require considerable specialist effort. AI assistance can help users describe what they need and turn that request into something they can review.
With Seafront IGA, users can work in natural language to explore access, prepare requests and assist with configuration. For example, an administrator can describe an integration requirement and review the configuration prepared with AI assistance before validation and activation.
The same principle applies to everyday AI-assisted operation. AI can help explain existing access or prepare a proposed change, while the platform applies the relevant policies and approval process.
This makes human-in-the-loop operation concrete: people can inspect and verify proposed changes, with governance decisions recorded for later review.
Give teams and leaders room to innovate
The presentations at State of Identity Helsinki also highlighted the need for organisations to innovate and explore new ways of using AI. Teams and leaders need room to try new ideas, supported by a safe and practical way to access the tools and data they need.
Effective governance helps create those conditions. Teams can test whether an idea has value within clear boundaries, while leaders gain firsthand experience of where AI helps, where it falls short and what successful use requires.
A governed test environment can provide that opportunity. It should have a named owner, approved test identities, suitable data and permissions limited to the experiment. A clear end date and spending limits help keep the scope manageable.
Access must also be useful enough to support the test. If an experiment cannot reach the approved information or functions its task requires, it may tell the organisation little about the idea’s potential.
Leadership participation can be practical and focused: choose a relevant workflow, try it with the team and review the results against agreed quality criteria. That experience can inform decisions about further investment and deployment.
As an experiment progresses, its controls should develop with it. Moving into production requires evidence that the workflow performs reliably, an accountable operational owner and a review of the access it needs. Ending an unsuccessful experiment should include removing its permissions.
Seafront’s identity lifecycle and access governance capabilities support the identity and permission side of this process, alongside the organisation’s wider testing and security practices.
Make governance part of everyday AI use
AI-agent governance needs to continue beyond initial approval.
Agents change, business requirements evolve and experiments come to an end. Access reviews and lifecycle controls help organisations keep permissions aligned with the work that is actually being done.
Seafront IGA brings AI-agent identities into a shared governance platform, while AI-assisted configuration and operation help people manage that platform more easily. Together, these capabilities support a practical goal: making useful access available, maintaining clear responsibility and keeping people involved where their judgement is needed.